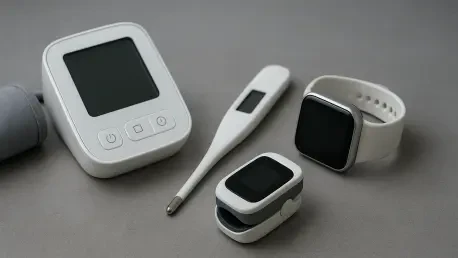
Comprehensive asset inventorying serves as the first critical step for healthcare providers looking to mitigate the risks associated with the quantum security gap. This initiative is becoming increasingly urgent as the disparity between standard enterprise technology and specialized medical systems widens, creating a significant point of failure in modern digital health infrastructure. While mainstream computing platforms have spent the period from 2026 to 2028 aggressively implementing post-quantum cryptography (PQC) to shield sensitive data from future decryption by quantum processors, the Internet of Medical Things (IoMT) remains largely static. Research reveals that only a tiny fraction of clinical hardware possesses the necessary architecture to support advanced cryptographic protocols like TLS 1.3 or SSH with quantum resistance. This leaves foundational medical equipment, including robotic surgery systems and diagnostic imaging arrays, operating on legacy security that is ill-equipped for the shifting landscape.
Longevity and Hardware Obstacles: Challenges in Clinical Settings
The specialized nature of clinical environments presents a unique challenge because the lifecycle of medical assets often spans over a decade, far exceeding the typical turnover seen in standard corporate IT departments. High-capital equipment like MRI scanners, laboratory automation systems, and computerized tomography units are designed for mechanical longevity rather than digital adaptability or cryptographic flexibility. Many of these devices rely on proprietary firmware or aging embedded operating systems that were never intended to handle the computational overhead required by post-quantum algorithms. Because these systems are mission-critical, any attempt to modify their core software carries significant clinical risk, potentially affecting patient safety or diagnostic accuracy. Consequently, many hospitals manage a fleet of technologically stagnant devices that provide essential care but lack the modern defensive capabilities required to stay secure in an evolving digital environment.
Furthermore, the process of upgrading or replacing these long-lived assets involves a complex undertaking that often clashes with the rapid pace of technological change. Procurement cycles in healthcare are frequently constrained by strict budgets and the need for rigorous regulatory validation, meaning that even when a vulnerability is identified, a solution may take years to deploy across an entire organization. Engineering and clinical staff must coordinate closely to ensure that any security intervention does not disrupt live workflows or invalidate the manufacturer’s certification. This logistical friction creates a bottleneck where security teams are unable to apply patches that would otherwise be routine in a standard server environment. As a result, the healthcare industry is effectively anchored to legacy cryptographic standards, making it one of the most difficult sectors to secure as quantum computing capabilities advance globally through 2028 and beyond.
The Immediate Risk: Harvest Now, Decrypt Later Tactics
The threat posed by quantum computing is not a distant concern but an active hazard due to the prevalence of “harvest now, decrypt later” strategies currently employed by sophisticated threat actors. In this scenario, cybercriminals intercept and store massive quantities of encrypted medical data today, waiting for the moment when quantum decryption power becomes sufficiently accessible to unlock it. For most industries, the shelf life of stolen data is relatively short, as passwords can be reset and credit cards can be canceled. However, the healthcare sector deals in permanent information; a patient’s genetic profile, chronic condition history, and detailed medical imagery remain relevant and sensitive for their entire lifetime. If this data is exfiltrated now, its eventual exposure a decade in the future would still constitute a catastrophic privacy violation, leading to immense legal liabilities and lasting damage to patient trust across the digital healthcare ecosystem.
This data-retention crisis is further exacerbated by the volume of sensitive information flowing through internet-exposed healthcare systems that currently lack post-quantum protections. While general IT systems are moving toward quantum-resistant standards, critical assets such as Electronic Medical Record systems and Picture Archiving and Communication Systems often remain exposed via outdated transport layer security. Research indicates that a substantial majority of these exposed systems do not yet support the protocols necessary for a secure transition, making them prime targets for interception. The permanence of medical data means that every weakly encrypted transmission today represents a long-term liability. This reality necessitates a shift in how healthcare providers view data protection, moving from a focus on temporary perimeter defense to a strategy that considers the security of information throughout its multi-decadal lifecycle in an increasingly powerful computing environment.
Strategic Defensive Shifts: Toward Resilience and Crypto-Agility
To address these systemic vulnerabilities, healthcare organizations must pivot toward a more holistic network architecture that emphasizes compensating controls rather than relying solely on device-level encryption. Since many legacy medical devices may never support native post-quantum cryptography, the implementation of rigorous network segmentation has become essential for isolating vulnerable hardware from external threats. By creating micro-perimeters around specific clinical departments or device types, hospitals can restrict traffic and monitor for anomalies that might indicate an interception attempt. Furthermore, the integration of advanced traffic inspection tools allows security teams to identify which devices are using deprecated cryptographic methods, enabling more targeted risk management strategies. This approach ensures that even if a device is technologically stagnant, the surrounding infrastructure provides a protective buffer that mitigates the risk of exfiltration.
The path forward required a fundamental change in how the industry approached equipment procurement, emphasizing “crypto-agility” as a mandatory requirement for all new medical technology. This shift ensured that future hardware was designed with the flexibility to receive cryptographic updates without requiring total replacement, effectively decoupling security software from the physical lifespan of the device. Healthcare providers began demanding greater transparency from manufacturers regarding the cryptographic foundations of their products, leading to a new era of collaboration between clinical engineers and cybersecurity researchers. By prioritizing these agile standards and reinforcing existing networks with robust segmentation, organizations successfully moved beyond the limitations of legacy hardware. The transition to post-quantum security was ultimately defined not just as a technical hurdle, but as an evolution in lifecycle management that protected patient confidentiality.