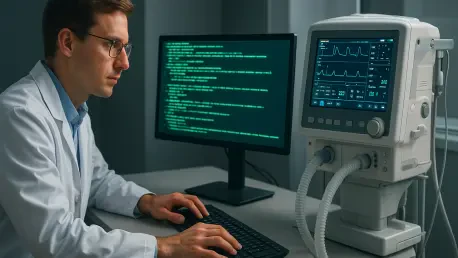
The FDA’s Total Product Lifecycle approach mandates that cybersecurity considerations begin at the initial design phase and continue until the device is decommissioned. This paradigm shift reflects the reality of 2026, where medical technology is no longer comprised of standalone hardware but exists as nodes within complex, high-stakes networks. Hospitals now rely on seamless data transmission between infusion pumps, bedside monitors, and electronic health records, often mediated by cloud-based analytics and mobile applications. While these interconnections improve patient outcomes through real-time interventions, they simultaneously create an expanded attack surface for malicious actors. Consequently, the regulatory environment has hardened, moving beyond simple checklists to demand comprehensive evidence of security-by-design. Manufacturers must now treat cybersecurity as a core engineering discipline, equivalent in importance to clinical efficacy. Failure to secure these digital pathways can lead to catastrophic failures, where a software exploit translates directly into patient harm, necessitating a robust, documented defense strategy that withstands the scrutiny of federal regulators and the evolving landscape of cyber threats.
The integration of advanced software into medical devices has brought about a transformation in patient care that was previously unimaginable. However, this evolution means that the digital integrity of a device is now inseparable from its medical safety. The modern healthcare environment is characterized by persistent threats, ranging from ransomware that can paralyze entire hospital systems to targeted exploits of specific device vulnerabilities. To address these risks, the documentation required for a premarket submission must provide a clear and compelling narrative of how a manufacturer identifies, mitigates, and manages cybersecurity risks. This narrative is built on several foundational pillars, including a detailed inventory of software components, sophisticated threat models, and comprehensive architecture views that illustrate how security controls are woven into the device’s fabric. By adhering to these requirements, manufacturers not only facilitate regulatory approval but also build a foundation of trust with the healthcare providers and patients who rely on their technology every day.
The Regulatory Framework and Lifecycle Approach
The current regulatory landscape is defined by a shift from reactive patching to proactive, lifecycle-long risk management. The primary touchstone for this approach is the updated guidance on Quality Management System considerations, which emphasizes that cybersecurity is not a static feature but a dynamic property of the device. Under Section 524B of the Federal Food, Drug, and Cosmetic Act, the agency has clarified its expectations for premarket submissions, requiring manufacturers to provide reasonable assurance that their devices are protected against cyber threats. This means that from the moment a developer writes the first line of code to the day a device is formally retired, the manufacturer remains responsible for its security posture. This lifecycle approach ensures that safety is maintained even as the threat environment evolves, requiring a continuous commitment to monitoring, patching, and updating systems to address newly discovered vulnerabilities that could compromise device performance.
This shift reflects a broader industry consensus that a cybersecurity failure is a fundamental patient safety issue rather than a mere data privacy concern. In the context of a connected medical device, a breach of integrity or availability can have immediate and devastating physical consequences. For instance, if a ventilator’s control system is compromised or if an infusion pump is remotely manipulated to deliver an incorrect dosage, the result is direct harm to the patient. Therefore, the FDA requires a clear narrative of risk mitigation that goes beyond technical specifications to explain the clinical impact of potential failures. Documentation must demonstrate that the manufacturer has considered the environment in which the device will be used, the types of users who will interact with it, and the potential for multi-patient harm in the event of a system-wide breach. This level of transparency is essential for proving that a device remains safe and effective throughout its intended lifespan.
Software Bill of Materials: Visibility and Inventory
A Software Bill of Materials serves as the essential inventory for all software components within a medical device, acting much like a list of ingredients on a food label. This document identifies every piece of code, including internally developed logic, commercial off-the-shelf software, and various open-source libraries or operating system elements. In the current era of modular software development, very few programs are built entirely from scratch; instead, they are assembled from numerous third-party dependencies that each carry their own set of risks. The FDA mandates this inventory because it provides the visibility necessary to manage these dependencies effectively. Without an accurate and detailed list, a manufacturer may remain unaware that their device contains a vulnerable library, leaving a backdoor open for attackers to exploit well-known security flaws that have already been patched elsewhere.
The utility of a Software Bill of Materials extends far beyond the initial regulatory submission, functioning as a living document that supports the device through its entire operational life. It is a critical tool for vulnerability identification and rapid impact analysis. When a new “Zero-Day” vulnerability is announced in a popular open-source package, security teams can use the inventory to immediately determine which of their devices are affected and prioritize the development of a patch. This process is vital for maintaining the security of the healthcare ecosystem, as it allows for a coordinated and efficient response to emerging threats. Furthermore, the document must be updated whenever software is updated or patched, ensuring that the manufacturer always has an accurate record of what is running on their hardware. This ongoing maintenance is a cornerstone of the postmarket surveillance activities that the agency expects from all modern medical device manufacturers.
Threat Modeling: Analyzing Potential Attack Paths
Threat modeling is a systematic process that explains what could go wrong by identifying potential risks and determining the appropriate security controls to mitigate them. While the software inventory explains what components are present, the threat model analyzes how those components might be attacked. This process involves a detailed examination of the device’s interfaces, trust boundaries, and data flows to identify credible threats that could undermine safety or effectiveness. The FDA emphasizes that these models must be highly specific to the device’s intended use and environment. A diagnostic imaging system located in a secured hospital basement faces a very different threat profile than a wearable glucose monitor that connects to a patient’s smartphone over public Wi-Fi. By tailoring the threat model to the specific context of the device, manufacturers can ensure that their security measures are both appropriate and effective.
An effective threat model must address fundamental questions regarding authentication, data integrity, and secure communication protocols. It is not enough to simply list potential threats; the manufacturer must provide a clear link between each identified risk and a specific security control. This traceability is a vital component of the documentation, as it proves to regulators that security features were not added as an afterthought but were intentionally chosen to address real-world dangers. For example, if a threat model identifies the risk of unauthorized access to a device’s configuration settings, the documentation should point to specific controls like multi-factor authentication or cryptographically secured access tokens. This logical connection demonstrates a mature and thoughtful approach to security engineering, giving reviewers the confidence that the device has been designed to withstand sophisticated attempts to bypass its internal protections.
Security Architecture Views: Providing Context
Architecture views provide the necessary visual and descriptive context to understand how the software inventory and threat models integrate into a cohesive system. These views define the “trust boundaries” where data moves from potentially untrusted environments, such as a hospital network or the internet, into the device’s internal processing core. The guidance recommends four specific types of architecture views—Global System, Multi-Patient Harm, Updatability, and Security Use Case—to help reviewers follow the manufacturer’s technical logic. Each view serves a distinct purpose: the Global System view provides a high-level overview of connections, while the Multi-Patient Harm view identifies scenarios where a single breach could impact several patients at once. These diagrams are essential for illustrating how a device maintains its security posture during various clinical and operational states.
These architectural diagrams are more than just technical drawings; they represent the blueprint of a device’s defense strategy. By mapping out how components interact during critical procedures, such as an emergency override or a remote software update, manufacturers can demonstrate that they have implemented robust security barriers at every critical junction. For instance, the Updatability and Patchability view describes the secure pathway through which a manufacturer delivers code to the device, ensuring that only verified and signed updates are installed. This level of detail is necessary to prove that the device is resilient against attempts to inject malicious code or intercept sensitive patient data. By providing these views, manufacturers offer a transparent look into the internal workings of their systems, making it much easier for regulators to verify that the claimed security controls are actually functioning as intended within the broader system architecture.
The Interconnectivity of Documentation Elements
One of the most critical aspects of the current regulatory framework is the requirement that the software inventory, threat model, and architecture views be fully integrated into a single, cohesive feedback loop. These elements should never be treated as independent, siloed deliverables. Instead, they must inform and reinforce one another throughout the development process. For example, the architecture views define the system layout that the threat model then analyzes for weaknesses. Conversely, the findings of the threat model may necessitate changes to the architecture to include more robust security barriers. Meanwhile, the software inventory provides the specific technical details needed to evaluate the vulnerabilities associated with third-party components identified in the threat model. When these documents are synchronized, they create a comprehensive narrative that builds significant confidence in the device’s overall security posture.
This interconnectivity is essential for preventing documentation gaps that could otherwise lead to regulatory delays or scrutiny. If the names of components in the software inventory do not match those used in the threat model or architecture diagrams, it creates confusion and suggests a lack of coordination within the development team. A cohesive set of documents demonstrates that the manufacturer has a unified understanding of the device’s security and that the various engineering and quality teams are working in harmony. For instance, if a threat model identifies a risk of a “malicious update,” the architecture view should clearly show the secure update pathway, and the software inventory should list the specific cryptographic libraries used to verify digital signatures. This level of consistency and detail proves that the manufacturer has thoughtfully considered every aspect of the device’s security and has taken proactive steps to ensure its continued safety and effectiveness.
Industry Challenges: Moving toward Resilient Solutions
Many manufacturers historically struggled with maintaining consistency across their cybersecurity documentation, often leading to fragmented reports that failed to satisfy regulatory expectations. To overcome these common pitfalls, leading organizations established standardized naming conventions and designated clear ownership of security documents within their development teams. It became evident that providing mountains of raw technical data was counterproductive if that data was not organized to show the clear relationship between threats and mitigations. By focusing on clarity and structure, companies managed to avoid the “information overload” that often characterized early attempts at compliance. Furthermore, the integration of automated tools into the software build process allowed for the generation of real-time software inventories, ensuring that the documentation always accurately reflected the current state of the device’s code.
The industry eventually transitioned toward a model where cybersecurity was viewed as a primary pillar of patient safety rather than a secondary technical hurdle. Cross-functional collaboration between software engineers, quality assurance specialists, and regulatory professionals became the standard for developing resilient medical technology. Organizations that integrated threat modeling into the very first stages of product design found that they could address vulnerabilities much more cost-effectively than those who waited until the end of the development cycle. Looking ahead, the focus shifted toward the automation of security testing and the implementation of robust postmarket monitoring systems that could detect anomalies in real-time. By embracing these proactive strategies, manufacturers secured their place in a digital-first healthcare landscape, ensuring that their devices remained protected against the sophisticated threats of the future while continuing to deliver vital clinical benefits to patients worldwide.